About
Audits showed us the tool we needed to build.
Magier AI is a focused team of security and compliance engineers in Reston, Virginia. We help security and GRC teams build a defensible AI governance program.
Mission
AI Governance Without Spreadsheet Expertise
When security and GRC teams took on AI governance, they often had no dedicated tools. They tracked AI systems, matched them to framework controls, and built evidence on demand in spreadsheets. Records went stale, while audit packages came together under pressure the week before an audit.
Magier AI gives these teams the infrastructure they lack. Continuous discovery, not a manual sweep. Control mappings that shift with the inventory. Evidence assembled before 11 PM on submission eve.
Live visibility
Governance starts with a live inventory. Our platform keeps an up-to-date view of the AI tools active in your environment.
Built by assessors
Practitioners who prepared for ISO 42001 assessments and NIST AI RMF reviews shaped our mappings. We focus on what assessors look for.
Security first
We handle our data with the scrutiny we ask of customers. See how we store, process, and protect it on our Security page.
Team
Our team
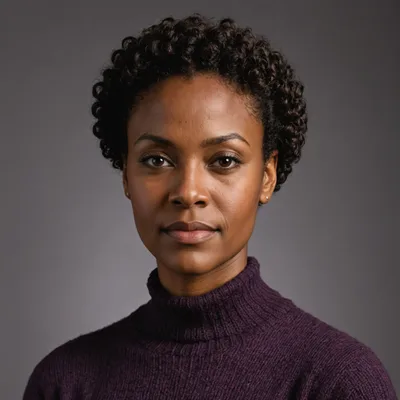
Ranice Brown
CEO & Co-Founder
Ranice focuses on security program management, audit readiness, and control framework implementation. She saw organizations repeatedly race to assemble compliance evidence after the fact, shaping her view that the process needed a better foundation.
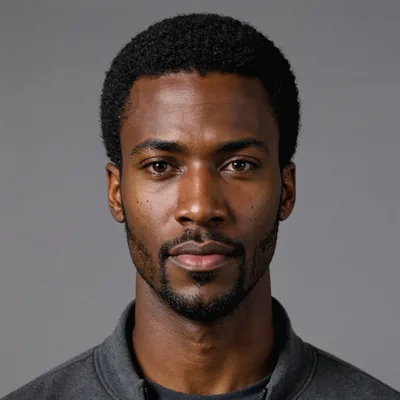
Darius Owens
CTO & Co-Founder
Darius builds security tooling at the infrastructure layer, with a focus on making visibility and enforcement work in complex enterprise environments. His background includes identity systems, network monitoring, and tooling designed to run quietly and reliably.
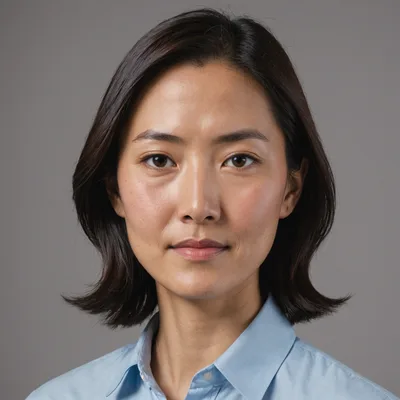
Yuki Chen
Head of Compliance Research
Yuki has deep expertise in AI governance standards and contributed to ISO 42001 working groups during the standard's development. Her background is in enterprise risk management and audit. She oversees framework accuracy and keeps our ISO 42001 and NIST AI RMF mappings current with every standard revision.
Our Story
Our beginning
Founded in 2024 in Reston, Virginia, Magier AI began with a team experienced in security architecture and compliance programs. We saw a recurring gap: security teams could not reliably tell which AI tools were active in their environments.
We bootstrapped by choice, staying close to customers instead of raising growth capital before proving the work useful. Each current feature grew from conversations with teams preparing for an ISO 42001 assessment or a board-level AI risk report with inadequate tools.
If you are a security or GRC practitioner facing an unmet workflow or framework need, tell us. Practitioner input is how the current product was built.
Work with us
A 30-minute walkthrough is the fastest way to see whether the platform covers the specific governance workflows your team needs.